
How Do You Break a Shift Cipher?

Seeking clarity on How Do You Break a Shift Cipher? We break down the key details supported by reliable sources.
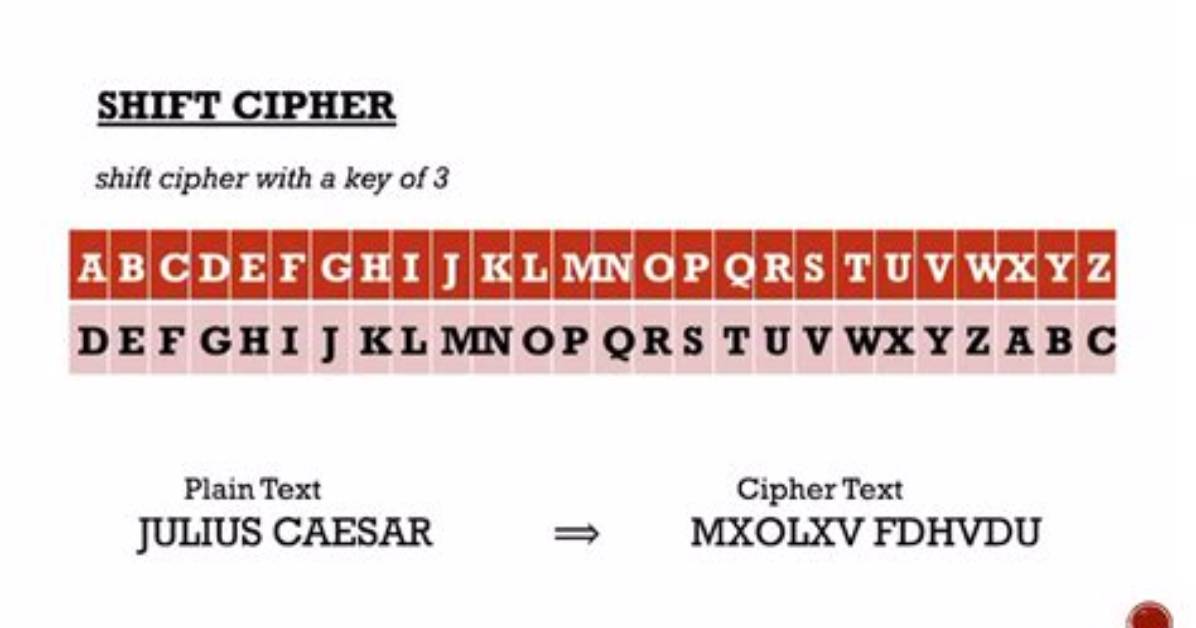
That is, given the intercepted ciphertext “RFWHZX HWFXXZX”, where we do not know what key has been used, but we do know that a Shift Cipher has been implemented, we must first try a key of 1, then a key of 2, then a key of 3 and so on, until a plaintext that makes sense is returned. For this ciphertext we would get:
Which is the most difficult cipher to break?
The Caesar cipher, while laughably easy to break for even the most novice modern cryptanalyst, forms a key part of the much more difficult to break Vigenère cipher. A cipher which took nearly 3 centuries to break and operates on interweaving different alphabets with several Caesar ciphers.
Is there a way to decrypt a Caesar shift cipher?
There is a general method for attacking all monoalphabetic ciphers called frequency analysis, which is discussed later. For the first two questions, use the given alphabet to encrypt the message using the Caesar Shift Cipher. For the second two questions, use the alphabet to decrypt the ciphertext.
Can a cryptanalyst crack a Caesar cipher code?
The cryptanalyst is totally unaware of the kind of cipher they are faced with. In all of the proposed scenarios, assuming that the cipher relies on a simple numerical shift, the code can very easily be cracked using a brute force attack (trying all possible shifts and determining which one works).
Maya is a hardware enthusiast who tests and reviews smart home devices, smartphones, wearables, and audio gear. She focuses on practical consumer value and build quality.
